Knowing isn't behaving
What a near-miss reminds us about keeping people safe from cyber threats.
By Frazer MacRobert, Senior Client Partner.
Early August, 2026, our team came within a ‘click’ of a serious mistake. I want to walk you through it, because the interesting part isn't that we caught it... It's how close we came to missing it.
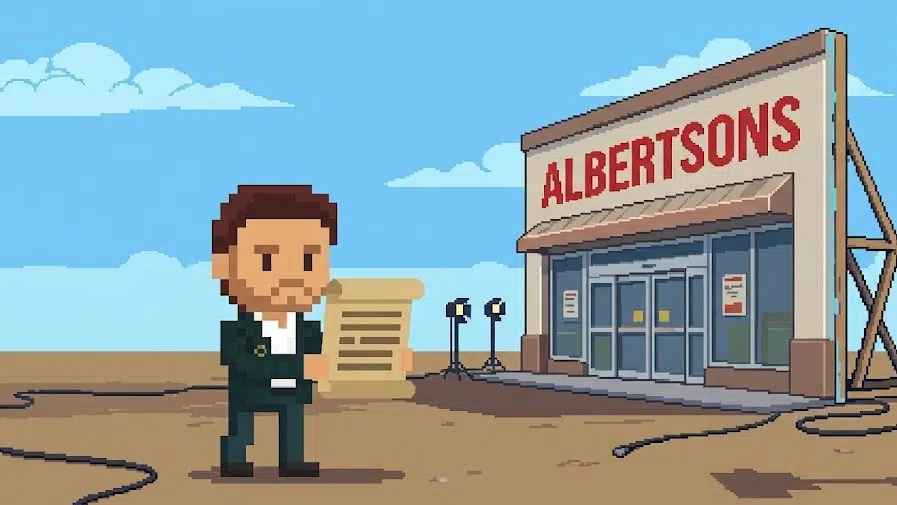
An enquiry landed in our inboxes from Albertsons, one of the largest grocers in the US. It seemed to be a warm, promising lead. We were pleased, and we replied with interest. Back came a mutual NDA to sign, shared over WeTransfer, with a note that the file was password protected for security. All very professional... All very normal.
Then our team looked closer. The email hadn't come from a domain Albertsons actually own. It came from ‘albertsongrpcompany.com’, a lookalike address that was registered only seven days earlier. It’s easy to access information on domains, but people rarely do it unless already suspicious.
We avoided the dodgy link, that could have let to spyware, a breach, a virus, ransonware... who knows. However it’s easy to overthink what would have happened if we’d got it wrong. As an agency, our work includes crafting cybersecurity campaigns for a living. Safety days, eLearning, campaign films, the lot. We know the signs better than most, and we still almost fell for it, because in that moment we wanted the email to be real.
A big-name enquiry is flattering. It's the kind of opportunity you hope for, and hope makes you generous with your attention. For a few minutes we weren't considering the security; We were reading like people who wanted good news. That is the exact gap every decent scam is built to exploit, and no amount of "check the sender address" closes it, because the failure doesn't happen in the part of your brain that stores the rules.
Knowing isn't behaving.
This is the uncomfortable truth about a lot of security awareness work. Knowing isn't behaving. People sit the training, pass the quiz, yet still make mistakes (like clicking dodgy links), because in the real moment they're busy, hopeful, distracted, or simply moving too fast to stop. Awareness tells people what's dangerous... It rarely changes what they do when it counts.
So the question we spend our time on isn't "do your people know the risks?" It's "when a risk turns up on an ordinary Thursday morning, will they behave differently?" Getting there takes more than a poster and a mandatory module.
Cyber Comms 101
Here are a few of the things that genuinely move the needle, and how we've built them.
Give safety comms a look and feel worth noticing. Messages about physical and digital safety protect your people and your business, so they can't fade into the wallpaper. They need to be seen, understood, talked about and acted on. What that looks like changes with the organisation and its personality. For our own brand, we once built muppet versions of the team, mixing the digital and the analogue and borrowing a Sesame Street principle: teach the character, don't patronise the viewer. For a sophisticated professional services firm, we designed intricate glitch textures that deliberately interrupted business-as-usual comms and made people stop. For a global law firm, we went somewhere more abstract, drawing parallels from the natural world so the work stood apart from everything else in the inbox, with a considered message behind every image, enough to make people pause, ask a question, and arrive at a deeper answer themselves.
Build learning people lean into. Most cyber eLearning is a compliance checkpoint people endure. We treat it as an employee experience. By designing around what our audience needs to know, feel and do, we get people engaging with the material and leaving with real understanding and a clear path to act, rather than a completion tick and nothing changed.
Aim at a measurable behaviour, then choose the format. We've built campaigns across every size and budget: a roadshow of games and activities, an employee magazine takeover, a video podcast series, and plenty in between. The format is always the last decision. First we get specific about the end state we want for the audience, and what will genuinely appeal to them, because a campaign with no defined outcome is just noise with a logo on it.
Get leaders modelling it. Messaging only lands when it's authentic to the organisation and visibly backed by the people at the top. When a leader talks about cyber behaviour and acts on it themselves, it stops being an IT instruction and becomes how things are done here. That's why leadership workshops, facilitation packs and briefing materials so often make the difference between a campaign people notice and one they follow.
Next up, Cyber Month
October is Cyber Security Awareness Month, which makes now a good time to ask an honest question. If an email like ours had landed with your people at 10am on a busy Thursday, how would it have gone? If you're confident, brilliant. If you're less sure, that's worth knowing in August rather than finding out in the moment.
We're already helping a handful of organisations build their Cyber Month campaigns, and there's still time to make something with real cut-through before October. If you'd like to talk it through, I'd be glad to.
As for us, we've reported the lookalike domain so Albertsons are aware their name is being used. And we've had a fresh reminder of the thing we tell our clients: the people most certain it won't happen to them are usually the ones worth worrying about. Sit down, be humble.